SECURITY Signal 62
Non-repudiation highlighted as a key pillar in cybersecurity framework
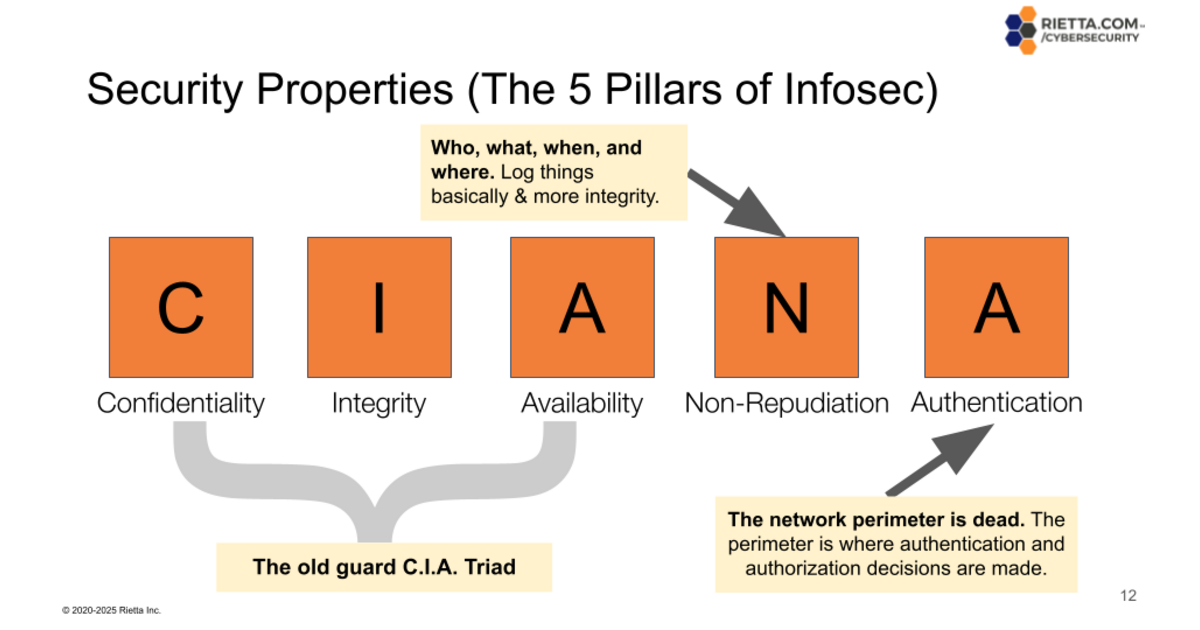 ↗
Non-repudiation is identified as one of the five foundational properties in the CIANA framework for information assurance.
Understanding non-repudiation is crucial for engineers working on security systems. It establishes accountability and traceability for actions taken within digital environments. Balancing non-repudiation with privacy regulations like GDPR and CCPA is essential to ensure compliance while maintaining security.
Written by elseif from the cluster below · every claim links back to a sourceThe three things worth knowing
Non-repudiation allows for verifying who performed an action in a system.
It must be balanced against privacy concerns to avoid data leaks.
Sufficient logging and monitoring are essential components of effective non-repudiation.
THE READ
What the cluster adds up to.
The recognition of non-repudiation as a foundational property in cybersecurity emphasizes its critical role in ensuring accountability for digital actions. This principle is particularly important in environments where understanding the source of actions can prevent fraud and enhance security measures.
Implementing effective non-repudiation controls can involve significant costs in terms of both time and resources. Engineers may need to invest in robust logging systems and auditing processes to ensure that they can provide proof of actions taken within their systems.
As organizations navigate the complexities of privacy regulations like GDPR and CCPA, they must find a balance between logging sufficient data to ensure non-repudiation and protecting users' privacy. Failing to do so could expose organizations to legal risks and undermine user trust.
Non-repudiation is sometimes at odds with privacy-centric principles, necessitating careful design in systems that handle sensitive information. Engineers must be cautious to prevent accidental exposure of private data while still maintaining thorough logging practices.
The emphasis on non-repudiation aligns with industry standards like the OWASP Top 10, highlighting its importance in building secure applications. Ensuring that all necessary data is logged without compromising privacy is a challenge that must be addressed in modern cybersecurity strategies.
Written by elseif from the cluster below · checked for specifics the sources never containedTHE CLUSTER