SECURITY Signal 76
Security researcher publishes reverse-engineered Stuxnet source code on GitHub
 ↗
The released repository provides build instructions that let interested techies examine Stuxnet’s USB-based infection chain and its payload that manipulates Siemens PLCs to alter centrifuge speeds.
Publishing the source code makes the first known malware that caused physical damage openly available for study, highlighting the real-world impact of cyber weapons. The release also reveals the specific zero-day exploits and stolen certificates used, giving defenders concrete indicators to look for in similar attacks.
Written by elseif from the cluster below · every claim links back to a sourceThe three things worth knowing
The researcher reverse-engineered Stuxnet and uploaded the source code to a public GitHub repository.
Stuxnet used USB sticks with zero-day shortcuts, a Windows Print Spooler zero-day, and stolen Realtek/JMicron certificates to spread and evade detection.
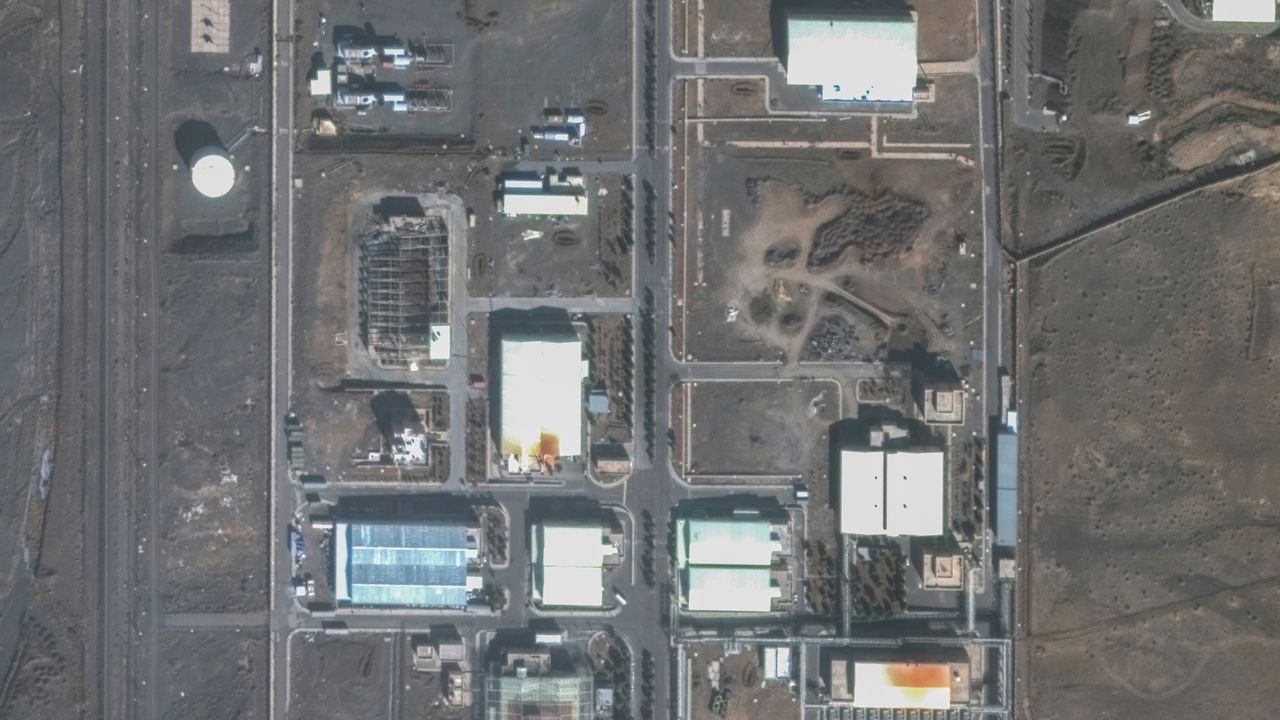
Its payload altered the frequency converters in Siemens PLCs at Iran’s Natanz plant, causing physical damage to centrifuge rotors.
THE READ
What the cluster adds up to.
A security researcher has reverse-engineered the Stuxnet worm and placed the resulting source code in a public GitHub repository. The repository includes build instructions that let interested techies compile and run the malware in an isolated environment. This makes the inner workings of the first known cyber weapon that caused physical damage openly accessible for study.
To execute the code safely, users must run it inside a Windows XP or Windows 7 virtual machine with all network connections disabled. They also need the appropriate Siemens engineering software and, ideally, the corresponding PLC hardware to observe the payload’s effect on frequency converters. Setting up this environment requires time, licensing for the Siemens tools, and careful isolation to prevent accidental spread. Beyond technical effort, sharing the code raises legal and ethical questions because the malware was designed for covert sabotage.
The worm includes a hard-coded self-destruct date of June 24, 2012, after which it ceases to execute. Its spreading mechanisms depend on zero-day exploits in older Windows versions and on code-signing certificates stolen from Realtek and JMicron. Without those specific vulnerabilities and certificates, the infection vectors will not function. Observing the payload’s effect on centrifuges further requires the Siemens WinCC/Step 7 software and the corresponding PLC hardware that Stuxnet targets.
Written by elseif from the cluster below · checked for specifics the sources never containedTHE CLUSTER