DATABASES Signal 20
Cold wallets isolate cryptocurrency private keys offline but remain vulnerable to hardware and software design flaws
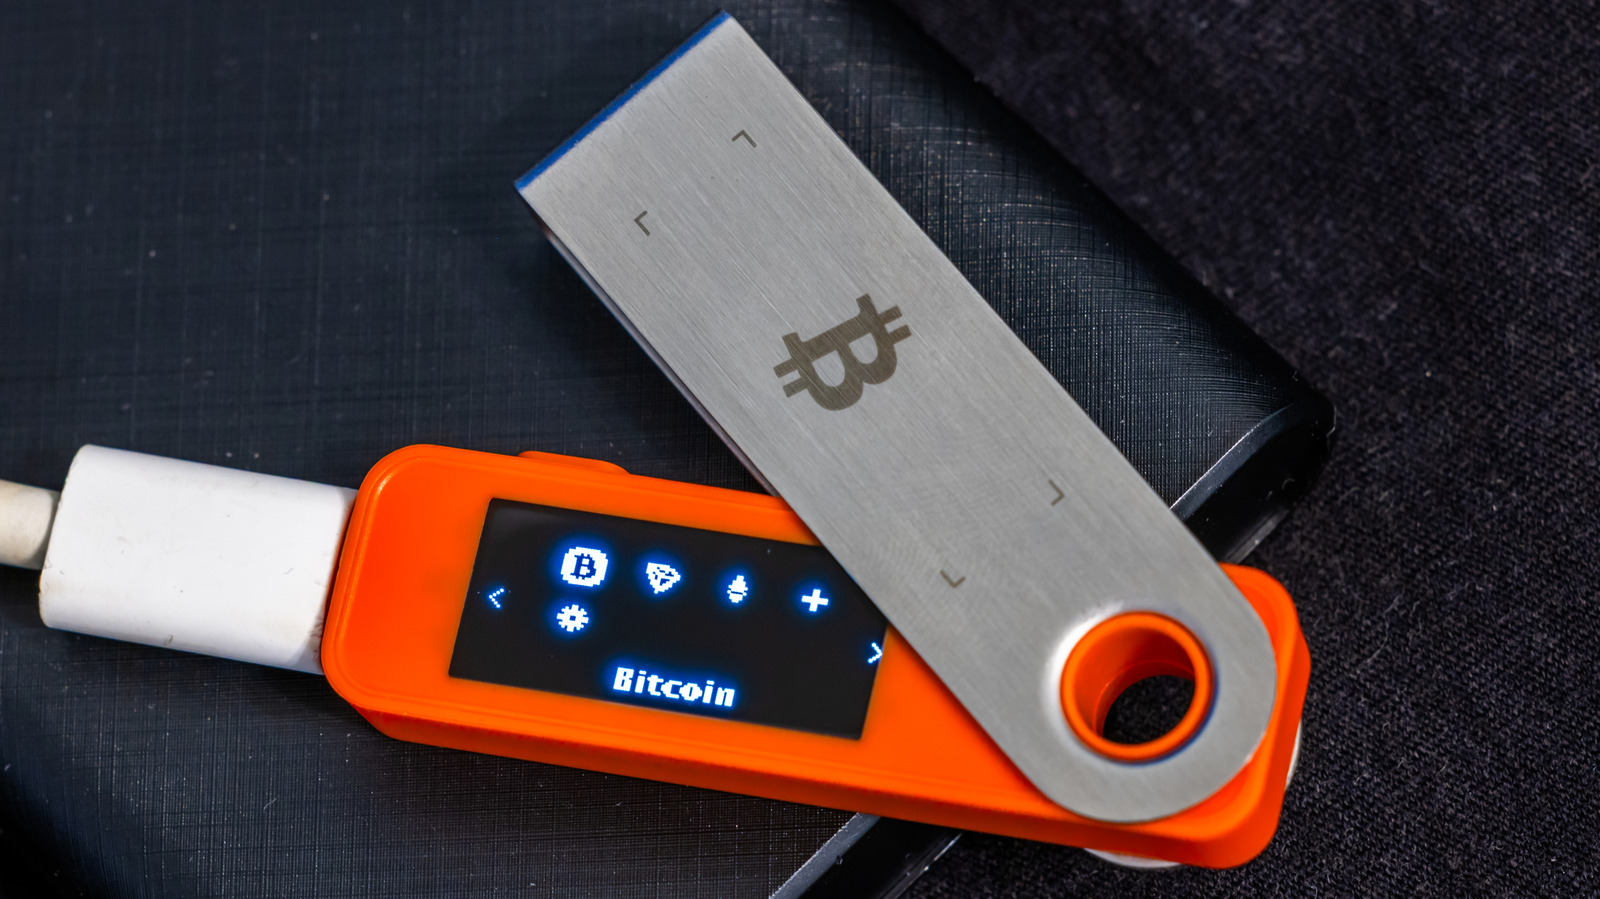 ↗
Hardware wallets keep cryptocurrency private keys offline on tamper-resistant chips, but design flaws like the Coldcard exploit demonstrate they are not entirely immune to attacks.
For engineers building cryptocurrency security systems, relying solely on offline key isolation is insufficient. Hardware and software design flaws can still expose funds to attackers, as demonstrated by recent exploits.
Written by elseif from the cluster below · every claim links back to a sourceThe three things worth knowing
Cold wallets keep private keys isolated on dedicated, offline hardware to protect against malware on connected devices.
Transaction signing occurs entirely on the hardware wallet, requiring manual confirmation on the device's own screen.
Despite tamper-resistant chips and PIN protection, hardware wallets remain vulnerable to design flaws that can lead to fund theft.
THE CLUSTER